A paper got accepted!

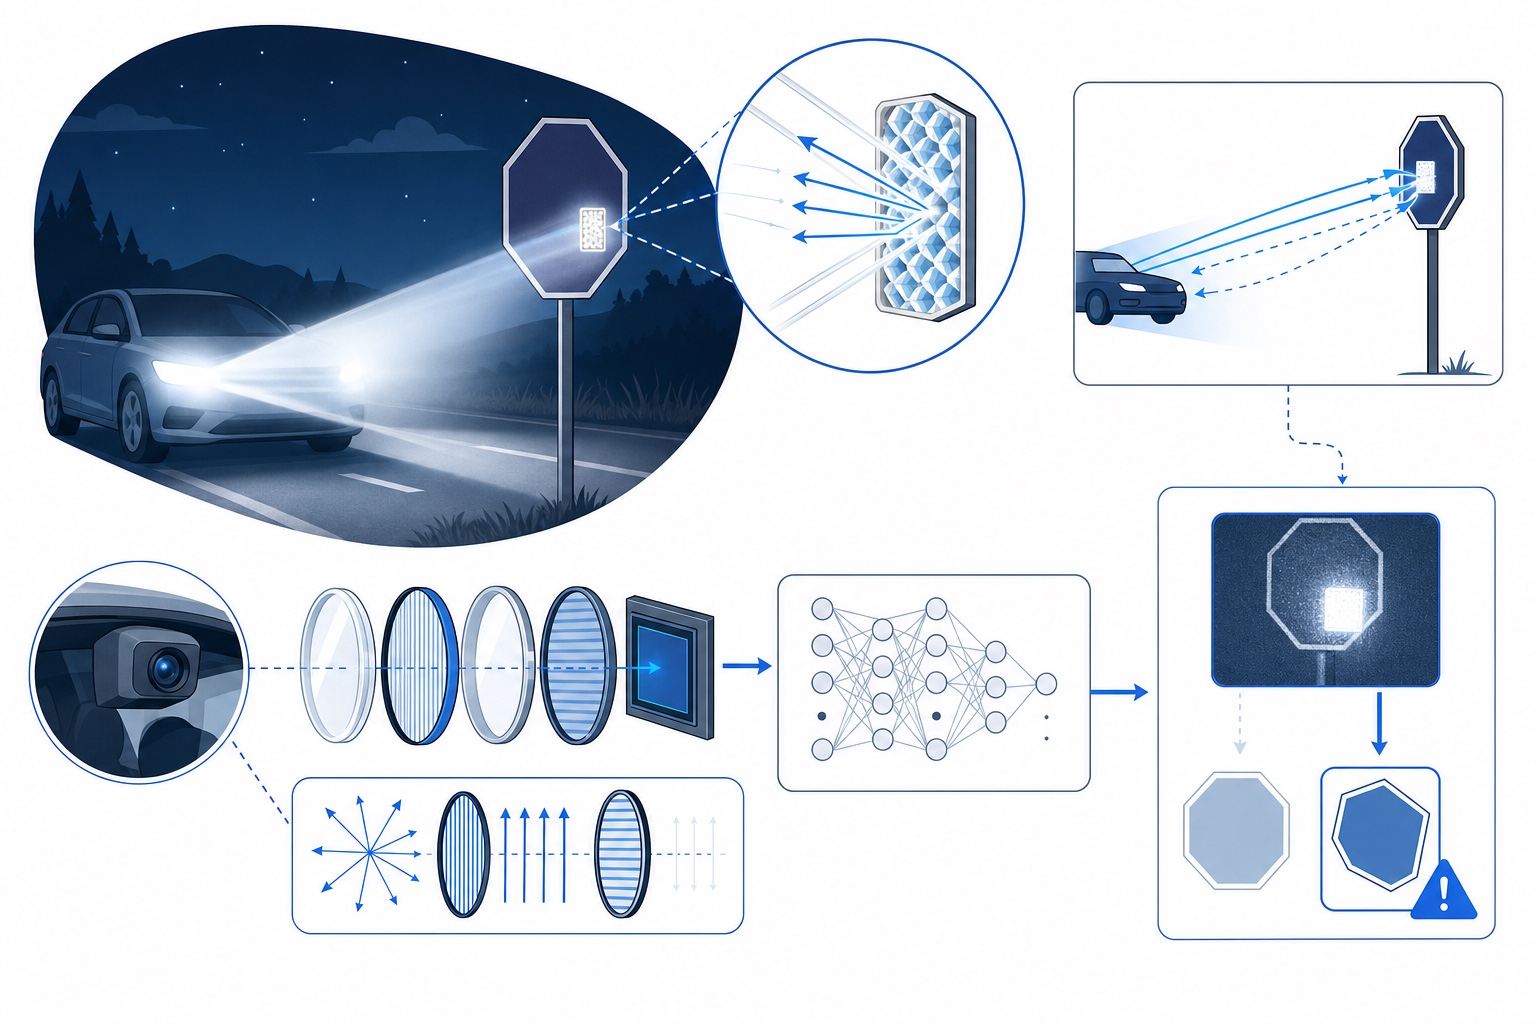
We are thrilled to announce that our conference paper entitled “Trapped by Their Own Light: Deployable and Stealth Retroreflective Patch Attacks on Traffic Sign Recognition Systems” has been accepted for publication in The 42nd Annual Computer Security Applications Conference (ACSAC 2026). This work is a fruit of our collaboration with Keio University and the University of California, Irvine. Congratulations to Tsuruoka-kun and kudos to the entire team!

In this work, we propose the Adversarial Retroreflective Patch (ARP), a novel attack vector against Traffic Sign Recognition (TSR) systems that combines the high deployability of physical patches with the stealth of light-based attacks. ARP leverages retroreflective materials that remain inconspicuous under ambient light and are activated only by the victim vehicle’s own headlights. Through physics-based retroreflection modeling and black-box attack optimization, ARP achieves over a 90% attack success rate in dynamic driving scenarios and 60% against commercial TSR systems, while a human user study confirms stealthiness comparable to benign signs. We also design DPR Shield, a defense built from two strategically placed polarized filters, which achieves ≥75% defense success rates for stop signs and speed limit signs.

Go Tsuruoka, Takami Sato, Qi Alfred Chen, Kazuki Nomoto, Ryunosuke Kobayashi, Yuna Tanaka, and Tatsuya Mori, "Trapped by Their Own Light: Deployable and Stealth Retroreflective Patch Attacks on Traffic Sign Recognition Systems." In Proc. of The 42nd Annual Computer Security Applications Conference (ACSAC 2026), Los Angeles, CA, USA, Dec 2026. (Acceptance rate=98/507=19.3%)
New pages: two continuously updated paper lists

We have set up two new pages that track the research literature our group follows closely. Both lists are harvested from arXiv and refreshed automatically every week.

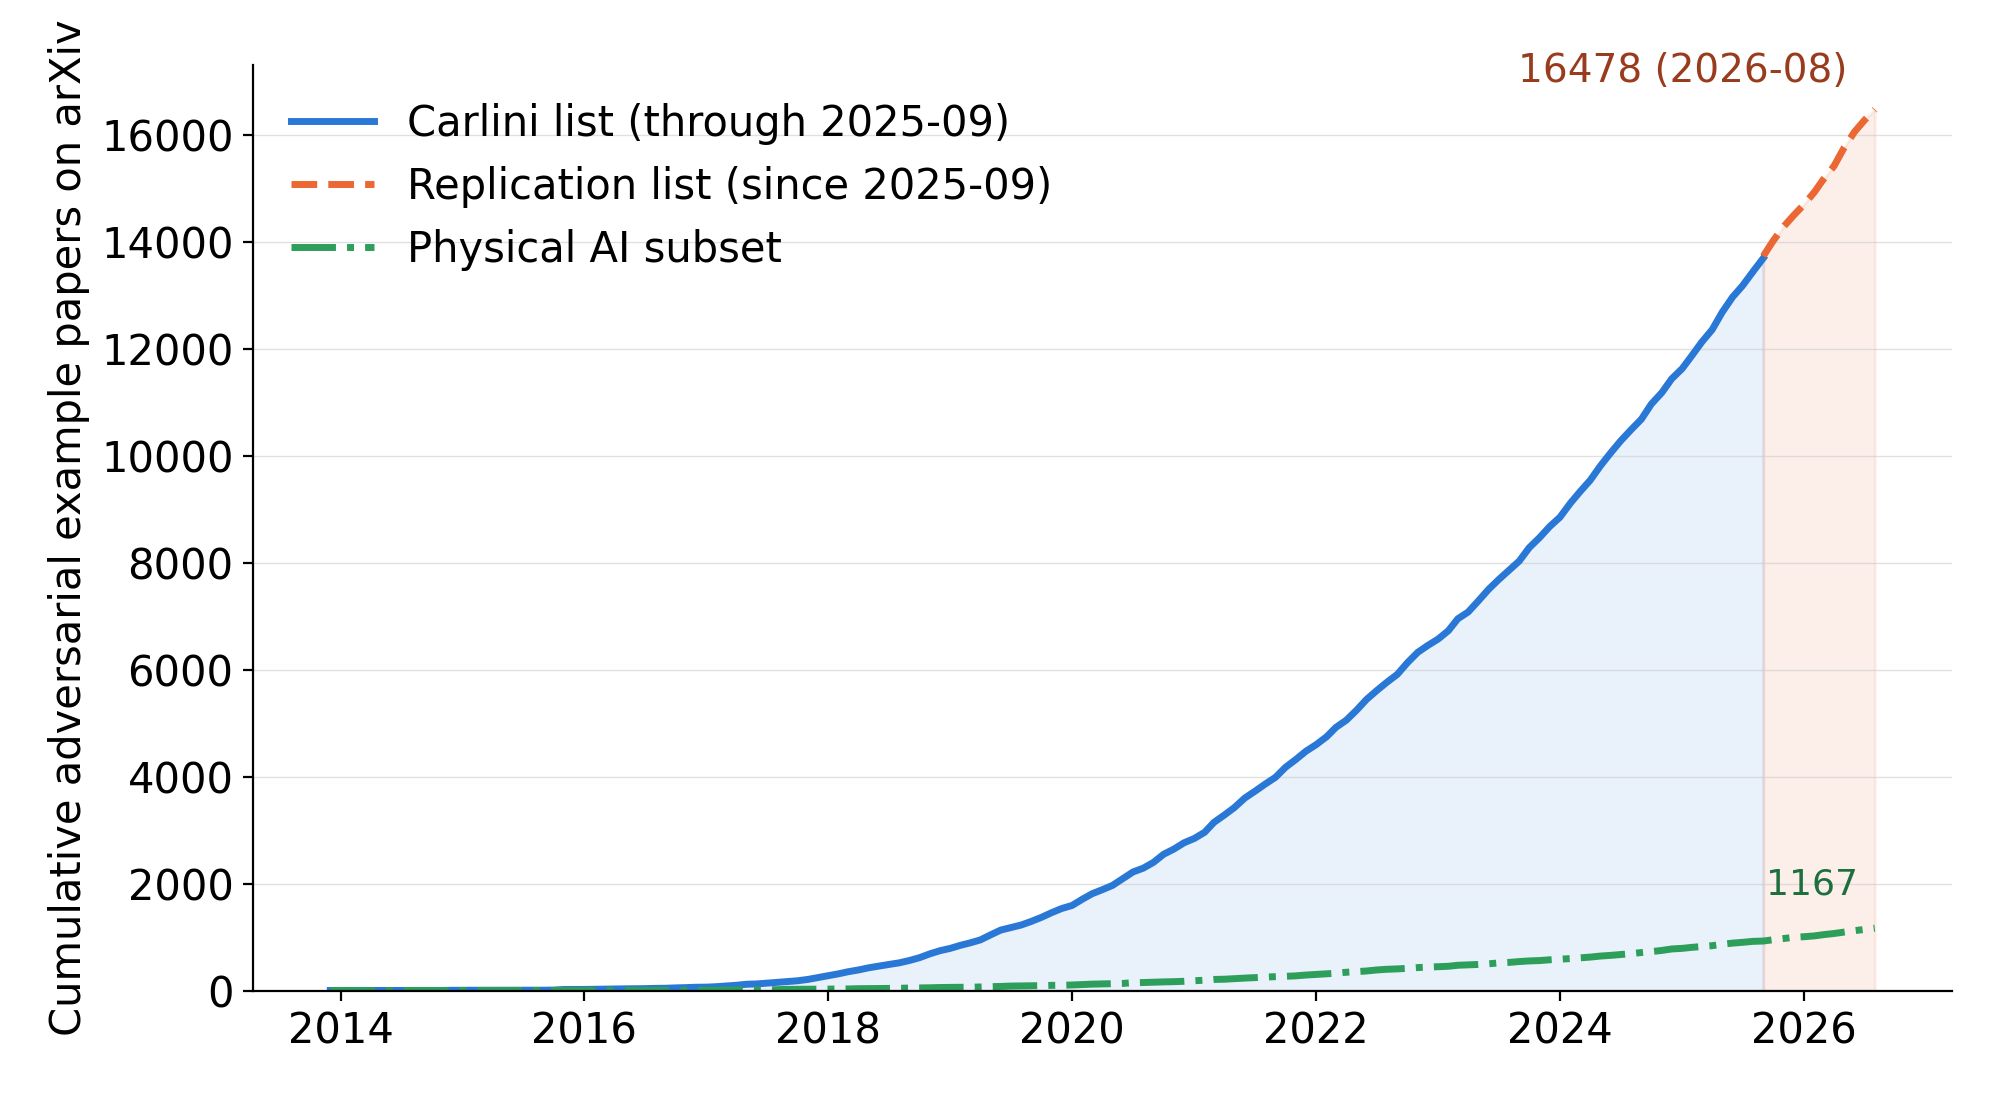
Adversarial Example Papers (Carlini list continuation): a continuation of Nicholas Carlini’s well-known “(A Complete) List of All Adversarial Example Papers”, which stopped updating in September 2025. Our replication covers arXiv submissions since then, selected by a classifier trained on the original 13,697-entry list.

Cumulative number of adversarial example papers on arXiv

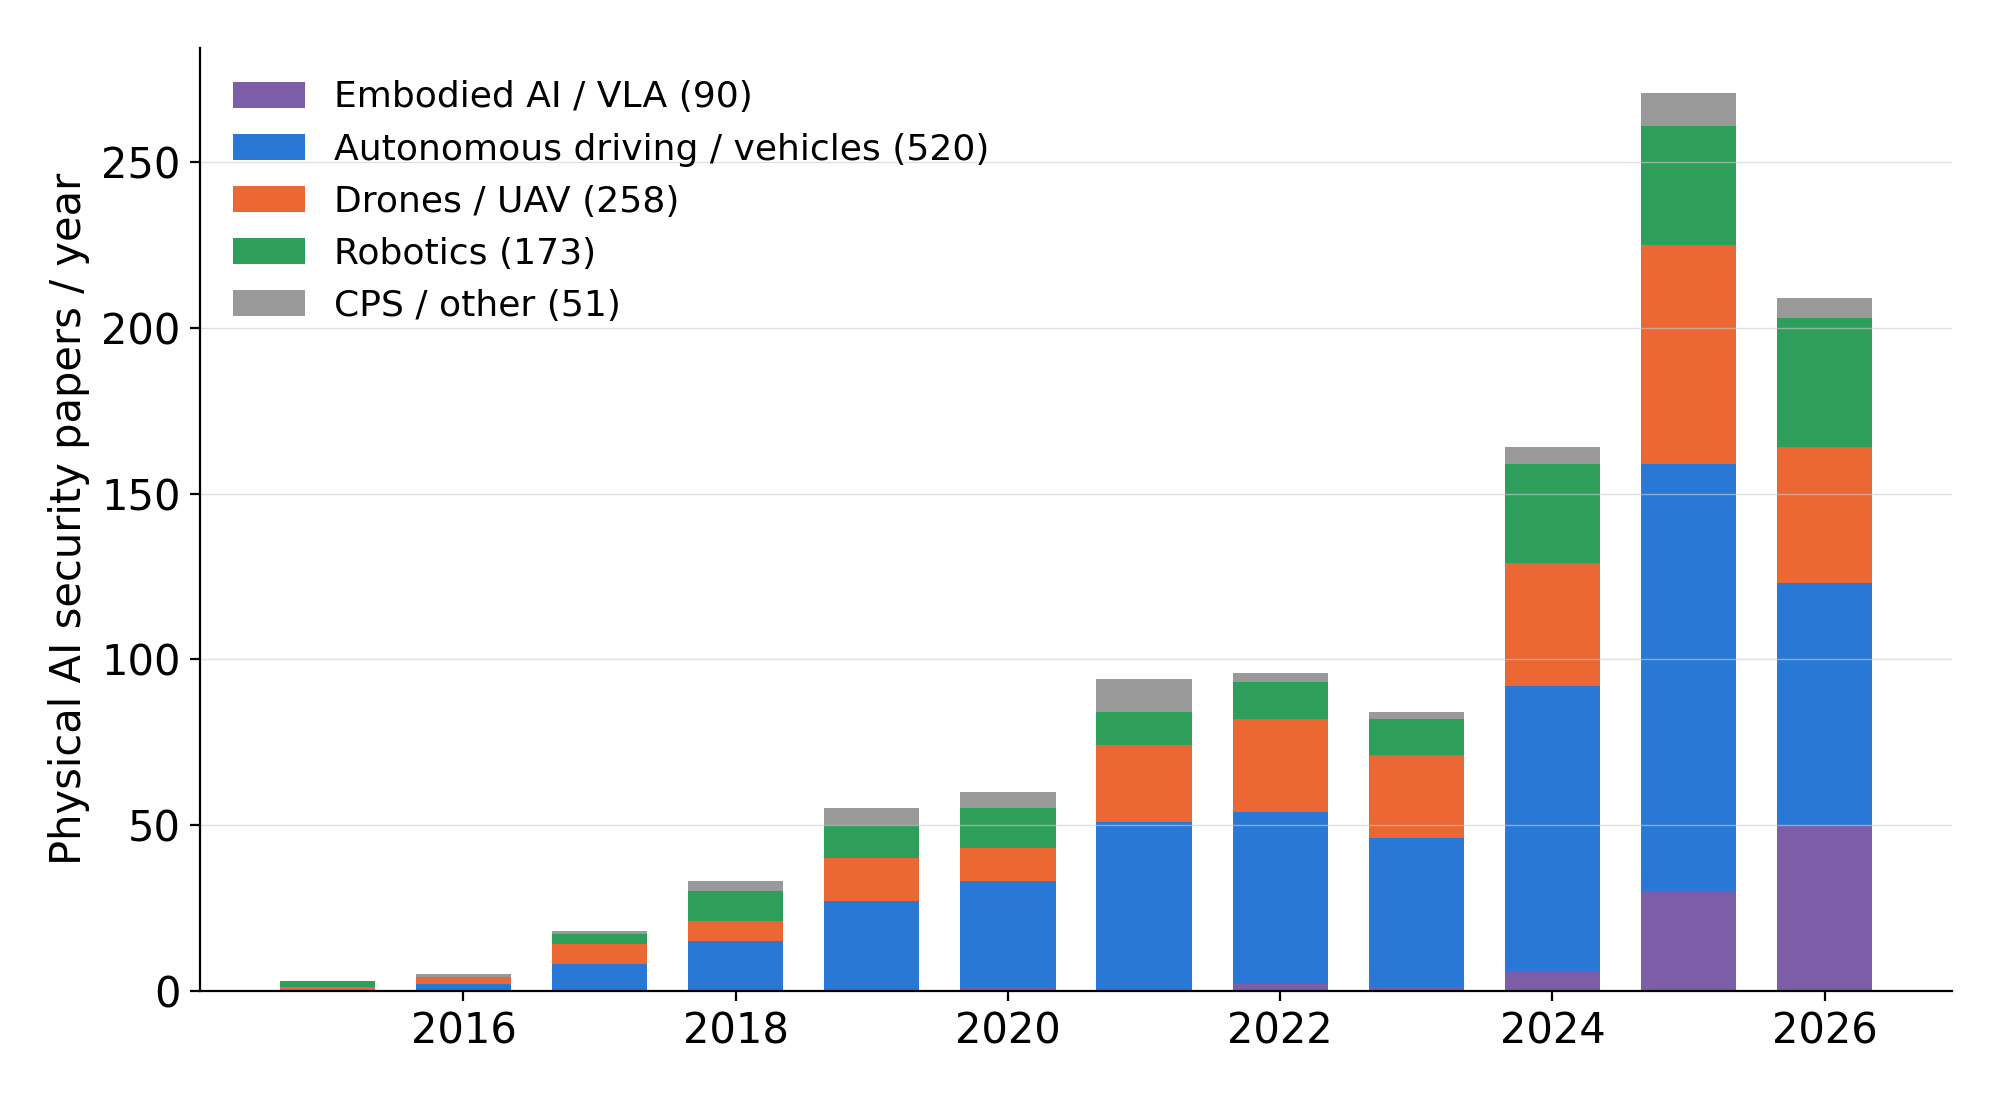
Physical AI Security Papers: a curated list of arXiv papers on the security (attacks and defenses) of AI-driven cyber-physical systems: autonomous driving, drones/UAV, robotics, and embodied AI. The list goes back to 2013 and is categorized by target platform.

Physical AI security papers per year by target category

Both pages are linked from the Projects menu. Comments and pointers to papers we may have missed are welcome.

A paper got accepted!

We are thrilled to announce that our conference paper entitled “Artistic Adversarial Examples: Graffiti-Based Adversarial Attacks on Traffic Sign Recognition” has been accepted for publication in The 28th International Conference on Information and Communications Security (ICICS 2026). This work is a fruit of our international collaboration with Politecnico di Milano. Congratulations to Zhuge-kun and kudos to the entire team!

Update (Oct 30, 2026): This paper received the Distinguished Paper Award at ICICS 2026! Read more

In this work, we propose artistic adversarial examples — adversarial patches crafted to look like ordinary street graffiti so that they blend naturally into urban scenes. Combining a graffiti-trained generative model with a two-stage optimization that couples white-box latent optimization and black-box placement refinement, our attack degrades traffic sign detection while keeping the perturbations visually plausible. Extensive experiments across digital, simulated, and physical settings show that the generated graffiti substantially disrupts traffic sign recognition, achieving up to a 72.8% attack success rate with an average confidence drop of 65.8%.

Zhenghao Michele Zhuge, Go Tsuruoka, Zhihe Zhang, Stefano Longari, Lachlan Moore, Stefano Zanero, and Tatsuya Mori, "Artistic Adversarial Examples: Graffiti-Based Adversarial Attacks on Traffic Sign Recognition." In Proc. of The 28th International Conference on Information and Communications Security (ICICS 2026), Fukui, Japan, Oct 2026.

A paper got accepted!

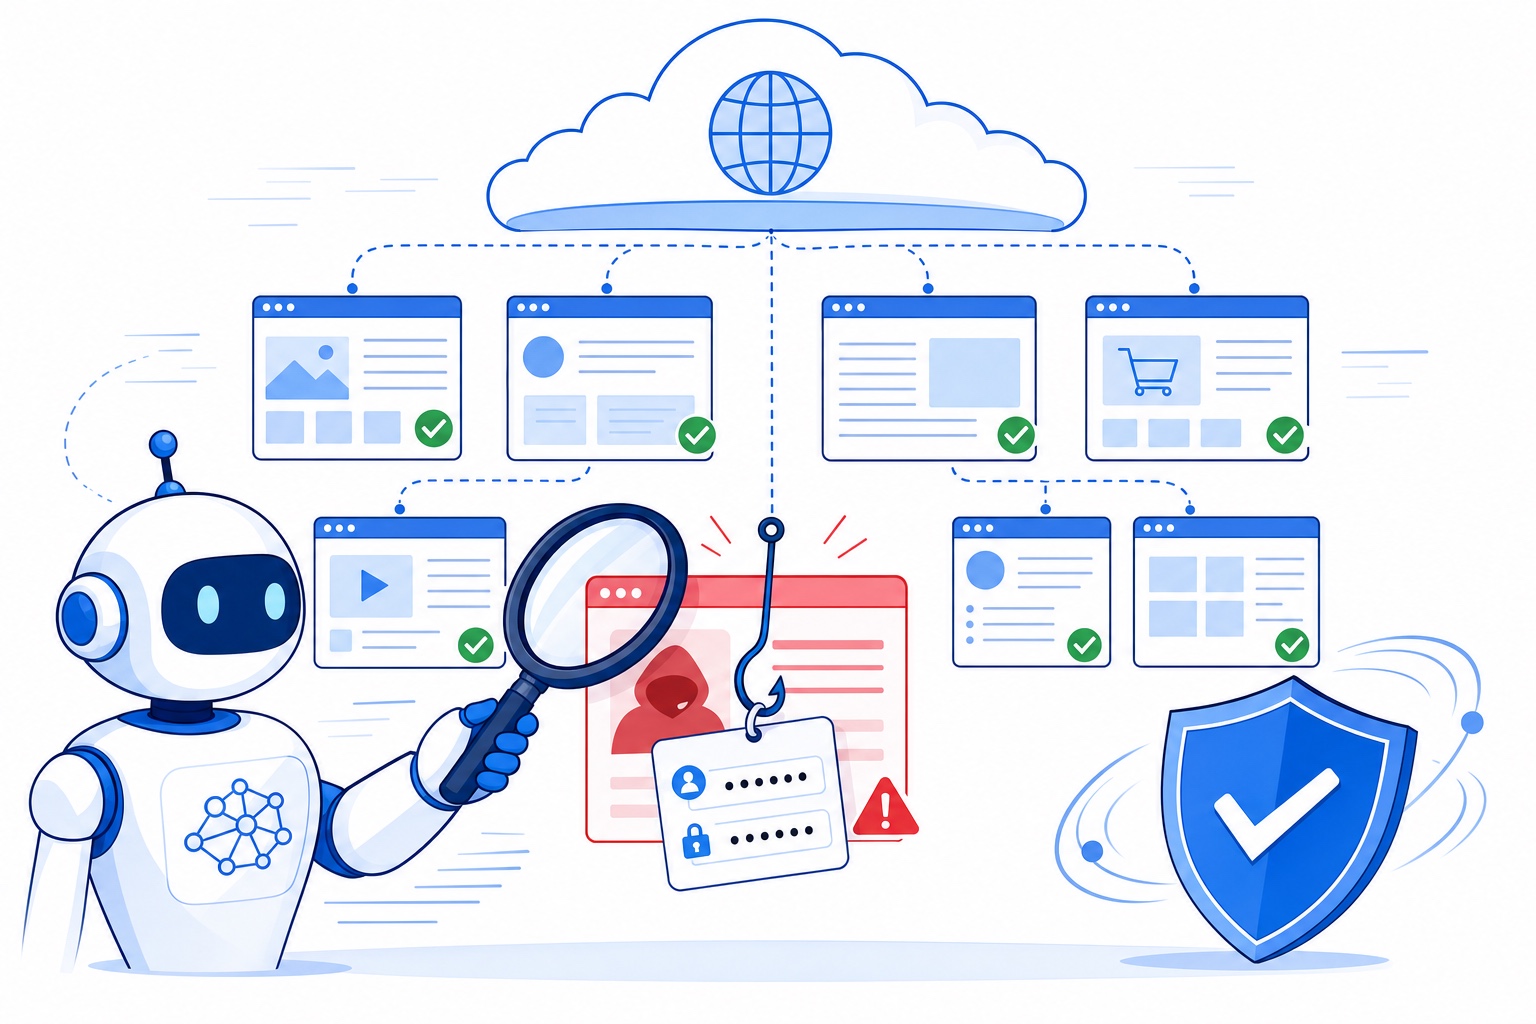
We are thrilled to announce that our conference paper entitled “Detecting Phishing on Shared-Domain Hosting Services Using LLM-Based Contextual Mismatch Reasoning” has been accepted for publication in The 21st International Conference on Availability, Reliability and Security (ARES 2026). Congratulations to Inuzuka-kun and kudos to the entire team!

In this work, we propose an LLM-based phishing detection workflow tailored to shared-domain hosting services (SHSs) such as free website builders, where benign and malicious pages coexist under the same provider-managed domain and conventional URL- and domain-based features break down. Our three-stage pipeline — Brand Analyzer, Content Analyzer, and Judge — reasons about the contextual mismatch between the brand a page claims to represent and the sensitive actions it prompts. Evaluated across ten SHSs with both commercial (GPT-4.1-mini) and open-source (Qwen3-8B) models, our system achieves high recall, outperforms state-of-the-art baselines including FreePhish and PhishLLM, and provides natural-language rationales that explain each verdict.

Sho Inuzuka, Takaaki Toda, Daiki Chiba, and Tatsuya Mori, "Detecting Phishing on Shared-Domain Hosting Services Using LLM-Based Contextual Mismatch Reasoning." In Proc. of The 21st International Conference on Availability, Reliability and Security (ARES 2026), Linköping, Sweden, Aug 2026.

A paper got accepted!

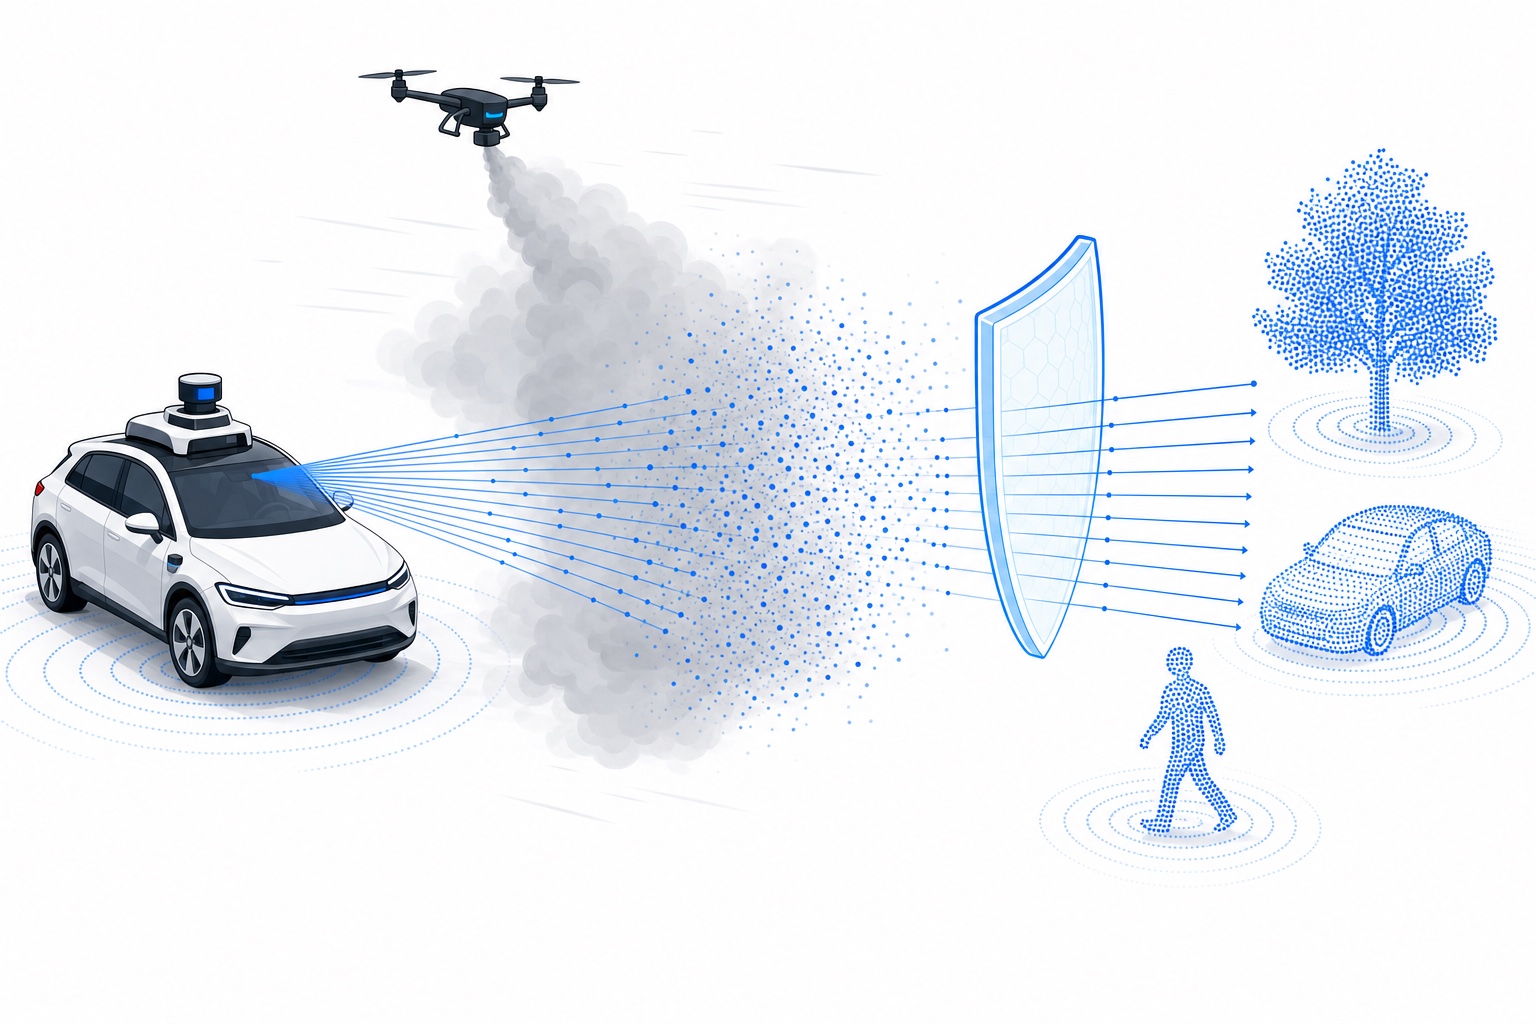
We are thrilled to announce that our journal paper entitled “Comprehensive Evaluation and Defense against Adversarial Fog Attacks on LiDAR-Based Autonomous Driving” has been accepted for publication in the Journal of Information Processing (JIP). Congratulations to Tanaka-kun and kudos to the entire team!

This paper is an extended journal version of our ACM AsiaCCS 2025 paper. In this work, we present a comprehensive evaluation of Adversarial Fog Attacks (AFA), which exploit vulnerabilities of point cloud preprocessing filters in LiDAR-based autonomous driving. We systematically analyze how environmental and attack parameters affect the attack effectiveness, physically validate the attack across multiple LiDAR models, and investigate post-detection avoidance behaviors together with practical defense strategies. The paper has been published in Vol. 34, pp. 748–774 (September 2026) and is available on J-STAGE.

Yuna Tanaka, Kazuki Nomoto, Ryunosuke Kobayashi, Go Tsuruoka, and Tatsuya Mori, "Comprehensive Evaluation and Defense against Adversarial Fog Attacks on LiDAR-Based Autonomous Driving." Journal of Information Processing, Vol. 34, pp. 748–774, Sep 2026. [J-STAGE]