A paper got accepted!

We are thrilled to announce that our conference paper entitled “Hidden in Plain Signs: Realistic Sticker Attacks on Production Traffic Sign Recognition Systems” has been accepted for publication in The 34th ISOC Network and Distributed System Security Symposium (NDSS 2027). This work is a fruit of our international collaboration with Politecnico di Milano. The research theme was conceived during the sabbatical stay of Prof. Mori at Politecnico di Milano in 2024. Congratulations to Bruzzese-kun and kudos to the entire team!

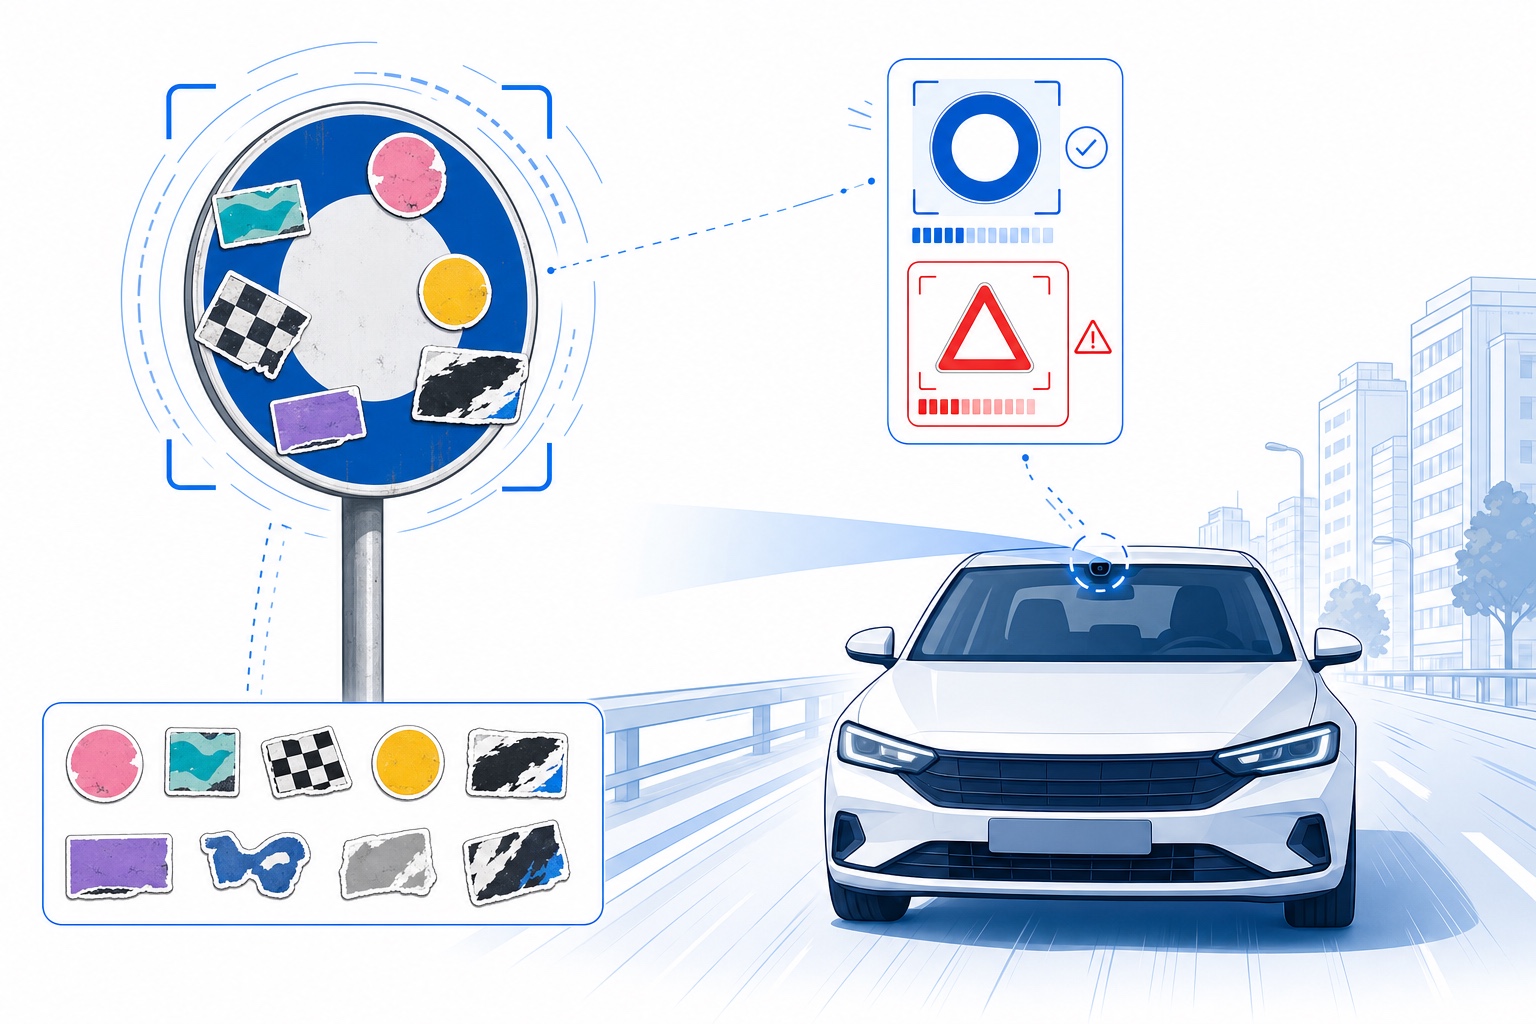
Traffic Sign Recognition (TSR) is a safety-critical component widely deployed in modern cars, while stickers and other artistic modifications on traffic signs have become commonplace in urban environments and are rarely perceived as suspicious. This coexistence creates a realistic attack surface. Existing adversarial attacks against TSR are rarely validated on production vehicles, often require expensive or conspicuous equipment, and typically target a narrow range of sign categories. To address this gap, we propose a black-box adversarial pipeline that leverages realistic urban sticker designs to induce misclassification and disappearance in neural-network-based TSR systems. Our method identifies sensitive regions on a target sign, selects stickers from a pre-defined pool, and iteratively optimizes their placement using an ensemble of state-of-the-art surrogate detectors within a high-fidelity rendering engine that simulates diverse driving conditions. We evaluate our approach using two distinct training datasets targeting 11 sign categories, and validate the resulting attacks through extensive real-world experiments on five commercial vehicles equipped with TSR systems. Across these vehicles, the proposed approach induces incorrect detections in 62% of cases on average, significantly outperforming state-of-the-art baselines, which reach only 19%. A human perception survey with over 100 participants further suggests that our perturbations are perceived as plausible urban artifacts, ensuring operational stealth. These findings demonstrate that adversarial examples extend beyond controlled laboratory settings and pose a credible, concrete, low-cost threat to real-world driving safety.

Luigi Bruzzese, Francesco Panebianco, Tatsuya Mori, Michele Carminati, Stefano Zanero, and Stefano Longari, "Hidden in Plain Signs: Realistic Sticker Attacks on Production Traffic Sign Recognition Systems." In Proc. of The 34th ISOC Network and Distributed System Security Symposium (NDSS 2027), Seoul, Republic of Korea, Mar 2027.
A paper got accepted!

We are thrilled to announce that our conference paper entitled “Privacy in Motion: Role Perspectives on Connected Vehicle Data Collection” has been accepted for publication in The 34th ISOC Network and Distributed System Security Symposium (NDSS 2027). Congratulations to Moore-kun and kudos to the entire team!

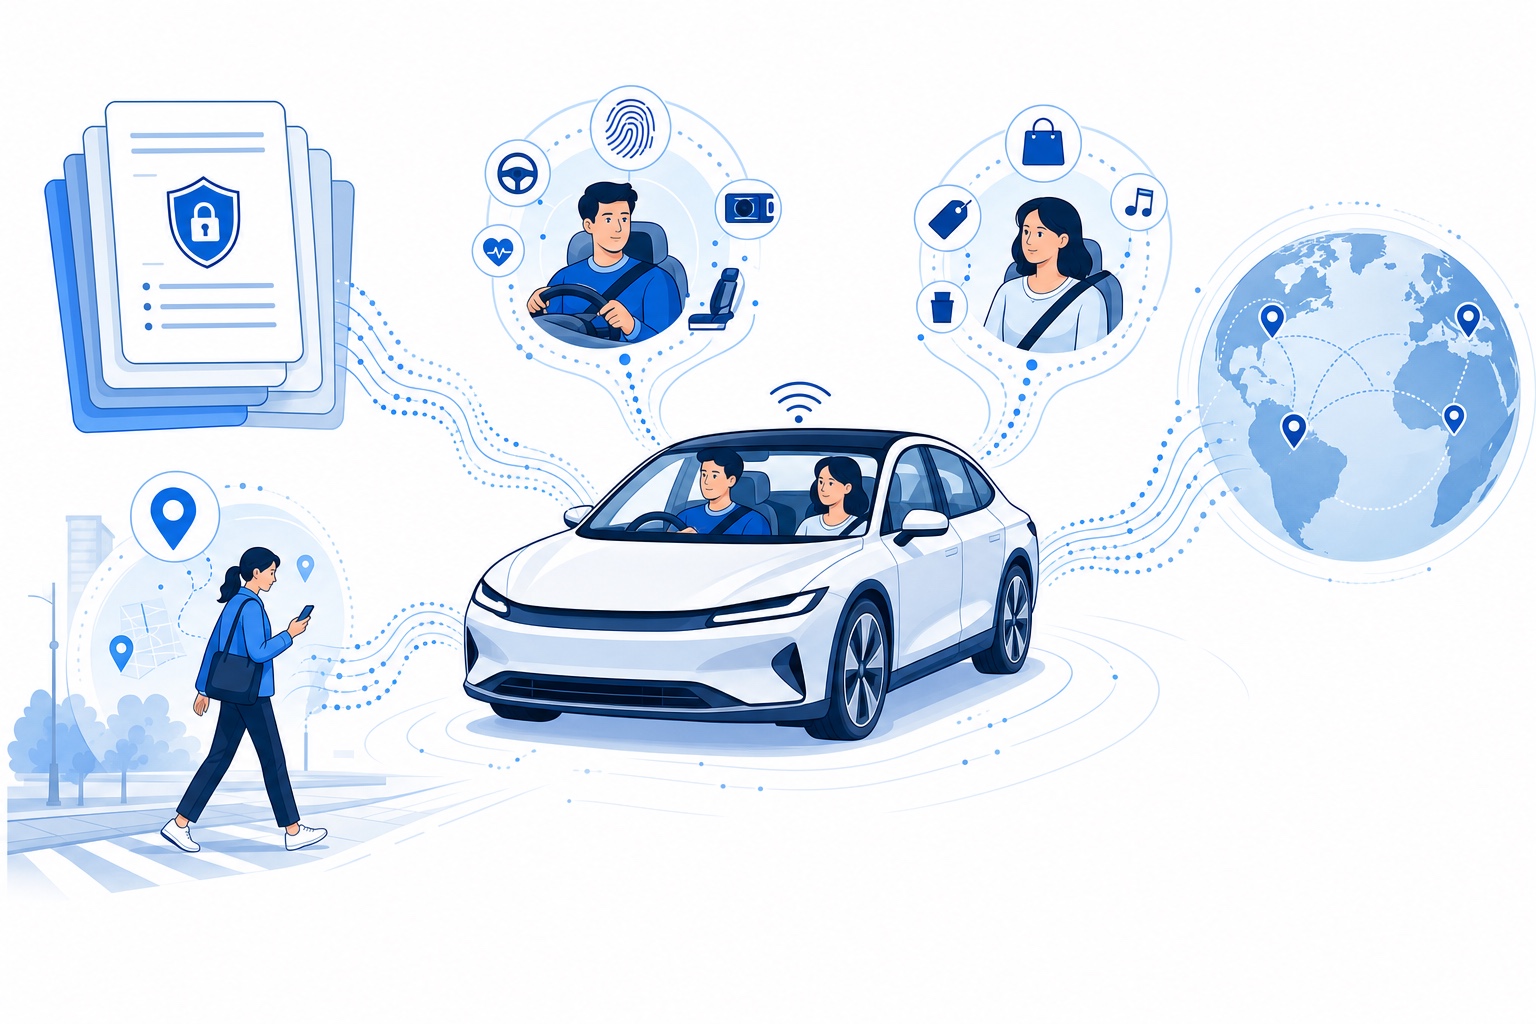
Connected vehicles have become data-intensive platforms that collect vast amounts of personal information not only from drivers but also from passengers and even nearby pedestrians, yet privacy protections and public understanding have not kept pace. In this work, we bridge the gap between what manufacturers disclose and how people perceive these practices through two complementary studies. In Study 1, we analyze the U.S. privacy policies of 17 major vehicle manufacturers, revealing extensive data collection, fragmented disclosures, and limited user control over third-party sharing. In Study 2, we survey 437 participants from the U.S., Germany, and China to examine comfort, expectations, and willingness to share data across the roles of driver, passenger, and pedestrian. We find that biometric and commercial data are perceived as particularly sensitive, that comfort with data collection varies significantly by role, and that a majority of users are willing to opt out of data collection. The results highlight a substantial disconnect between industry practices and public understanding, calling for clearer, role-aware, and culturally sensitive transparency mechanisms.

Lachlan Moore, Yinan Zhao, Rei Yamagishi, Allan Wirth, and Tatsuya Mori, "Privacy in Motion: Role Perspectives on Connected Vehicle Data Collection." In Proc. of The 34th ISOC Network and Distributed System Security Symposium (NDSS 2027), Seoul, Republic of Korea, Mar 2027.
A paper got accepted!

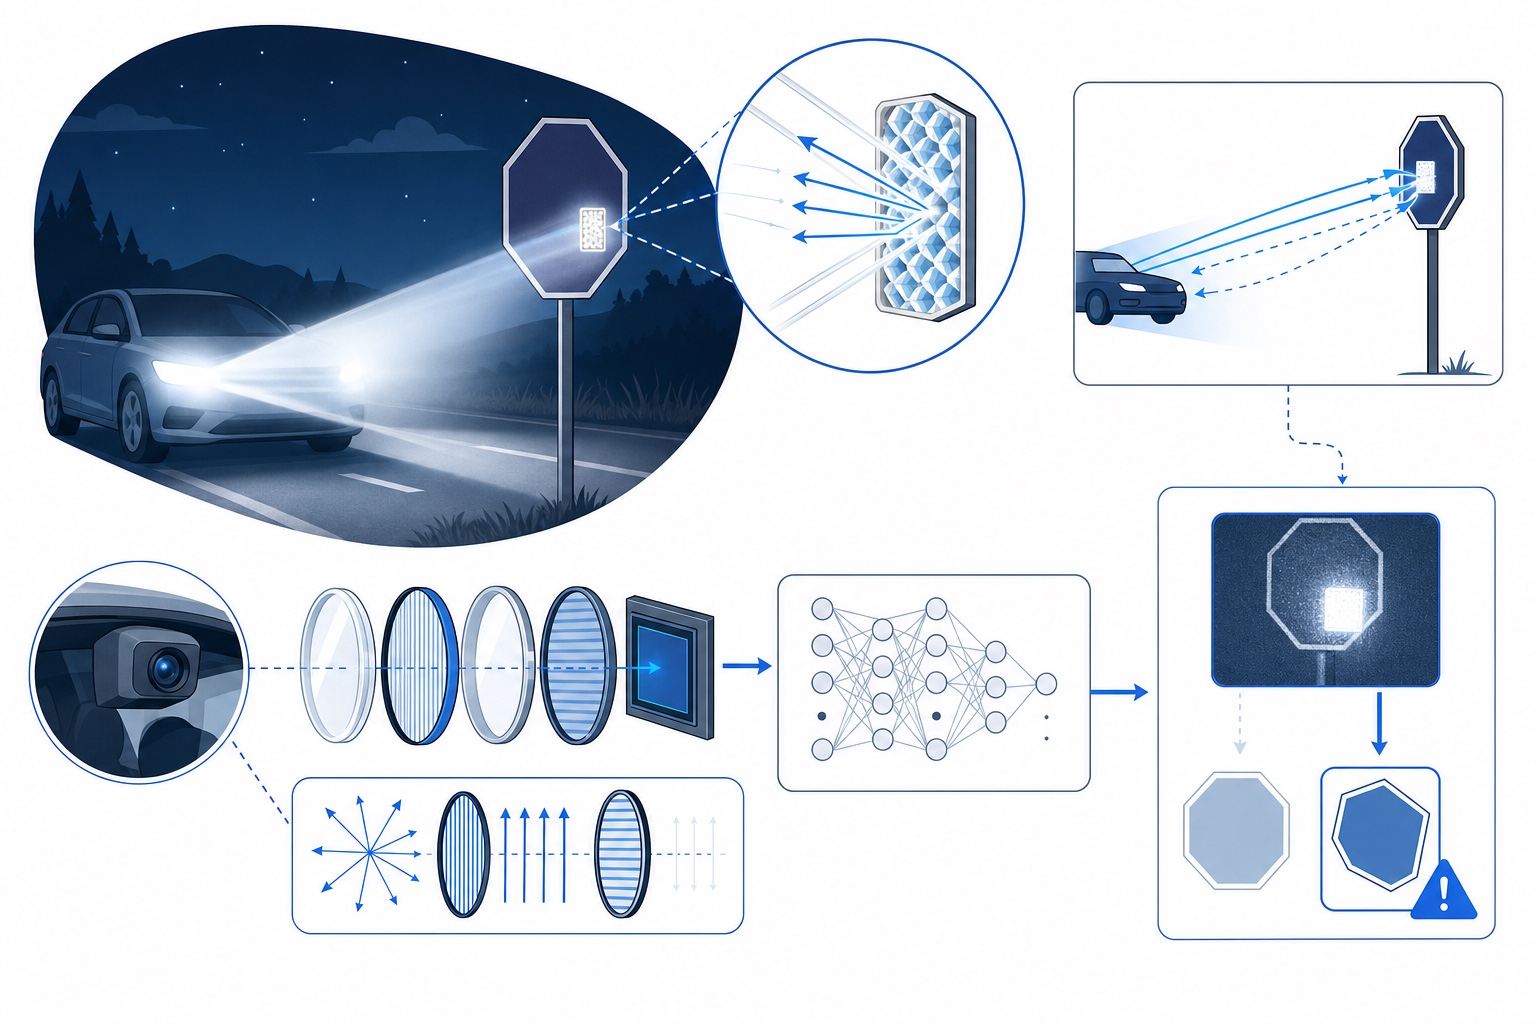
We are thrilled to announce that our conference paper entitled “Trapped by Their Own Light: Deployable and Stealth Retroreflective Patch Attacks on Traffic Sign Recognition Systems” has been accepted for publication in The 42nd Annual Computer Security Applications Conference (ACSAC 2026). This work is a fruit of our collaboration with Keio University and the University of California, Irvine. Congratulations to Tsuruoka-kun and kudos to the entire team!

In this work, we propose the Adversarial Retroreflective Patch (ARP), a novel attack vector against Traffic Sign Recognition (TSR) systems that combines the high deployability of physical patches with the stealth of light-based attacks. ARP leverages retroreflective materials that remain inconspicuous under ambient light and are activated only by the victim vehicle’s own headlights. Through physics-based retroreflection modeling and black-box attack optimization, ARP achieves over a 90% attack success rate in dynamic driving scenarios and 60% against commercial TSR systems, while a human user study confirms stealthiness comparable to benign signs. We also design DPR Shield, a defense built from two strategically placed polarized filters, which achieves ≥75% defense success rates for stop signs and speed limit signs.

Go Tsuruoka, Takami Sato, Qi Alfred Chen, Kazuki Nomoto, Ryunosuke Kobayashi, Yuna Tanaka, and Tatsuya Mori, "Trapped by Their Own Light: Deployable and Stealth Retroreflective Patch Attacks on Traffic Sign Recognition Systems." In Proc. of The 42nd Annual Computer Security Applications Conference (ACSAC 2026), Los Angeles, CA, USA, Dec 2026. (Acceptance rate=98/507=19.3%)

New pages: two continuously updated paper lists

We have set up two new pages that track the research literature our group follows closely. Both lists are harvested from arXiv and refreshed automatically every week.

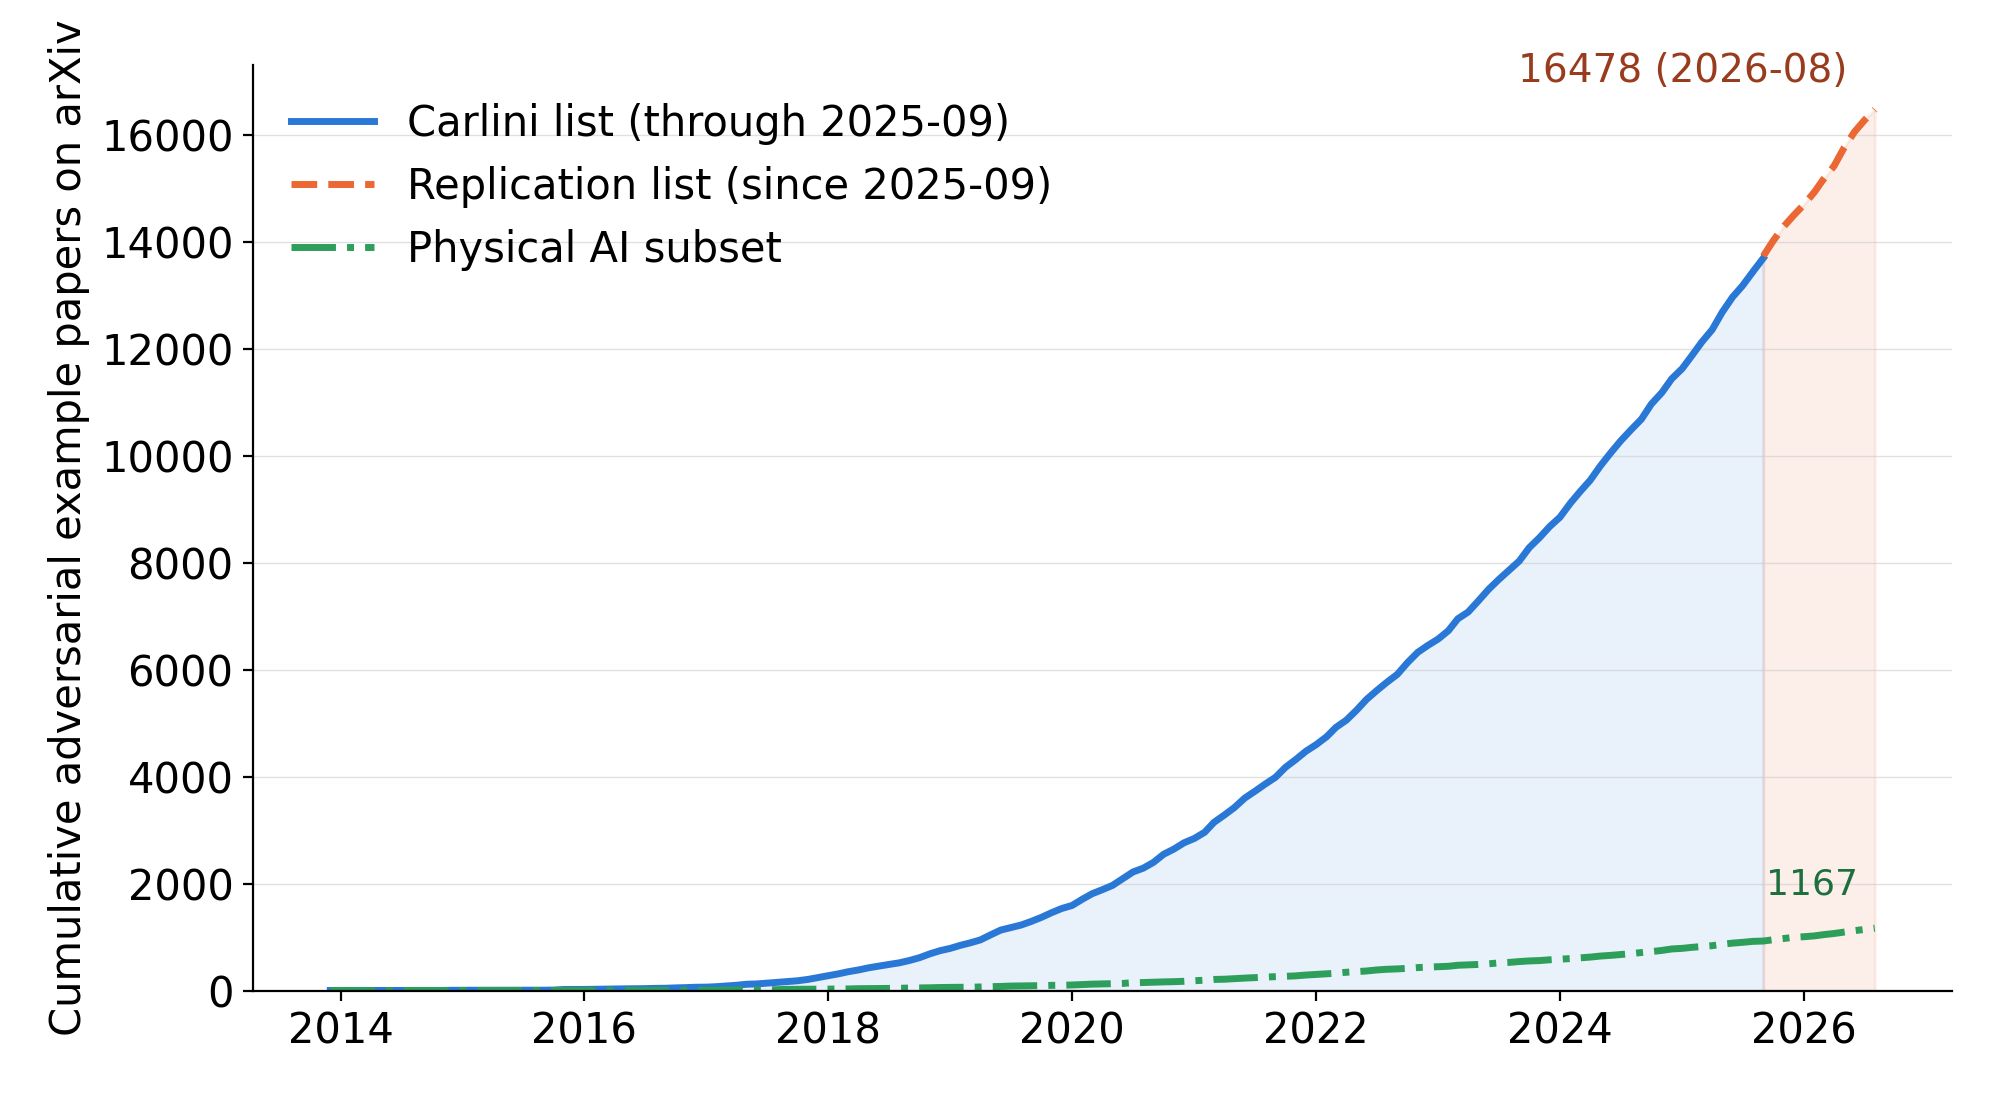
Adversarial Example Papers (Carlini list continuation): a continuation of Nicholas Carlini’s well-known “(A Complete) List of All Adversarial Example Papers”, which stopped updating in September 2025. Our replication covers arXiv submissions since then, selected by a classifier trained on the original 13,697-entry list.

Cumulative number of adversarial example papers on arXiv

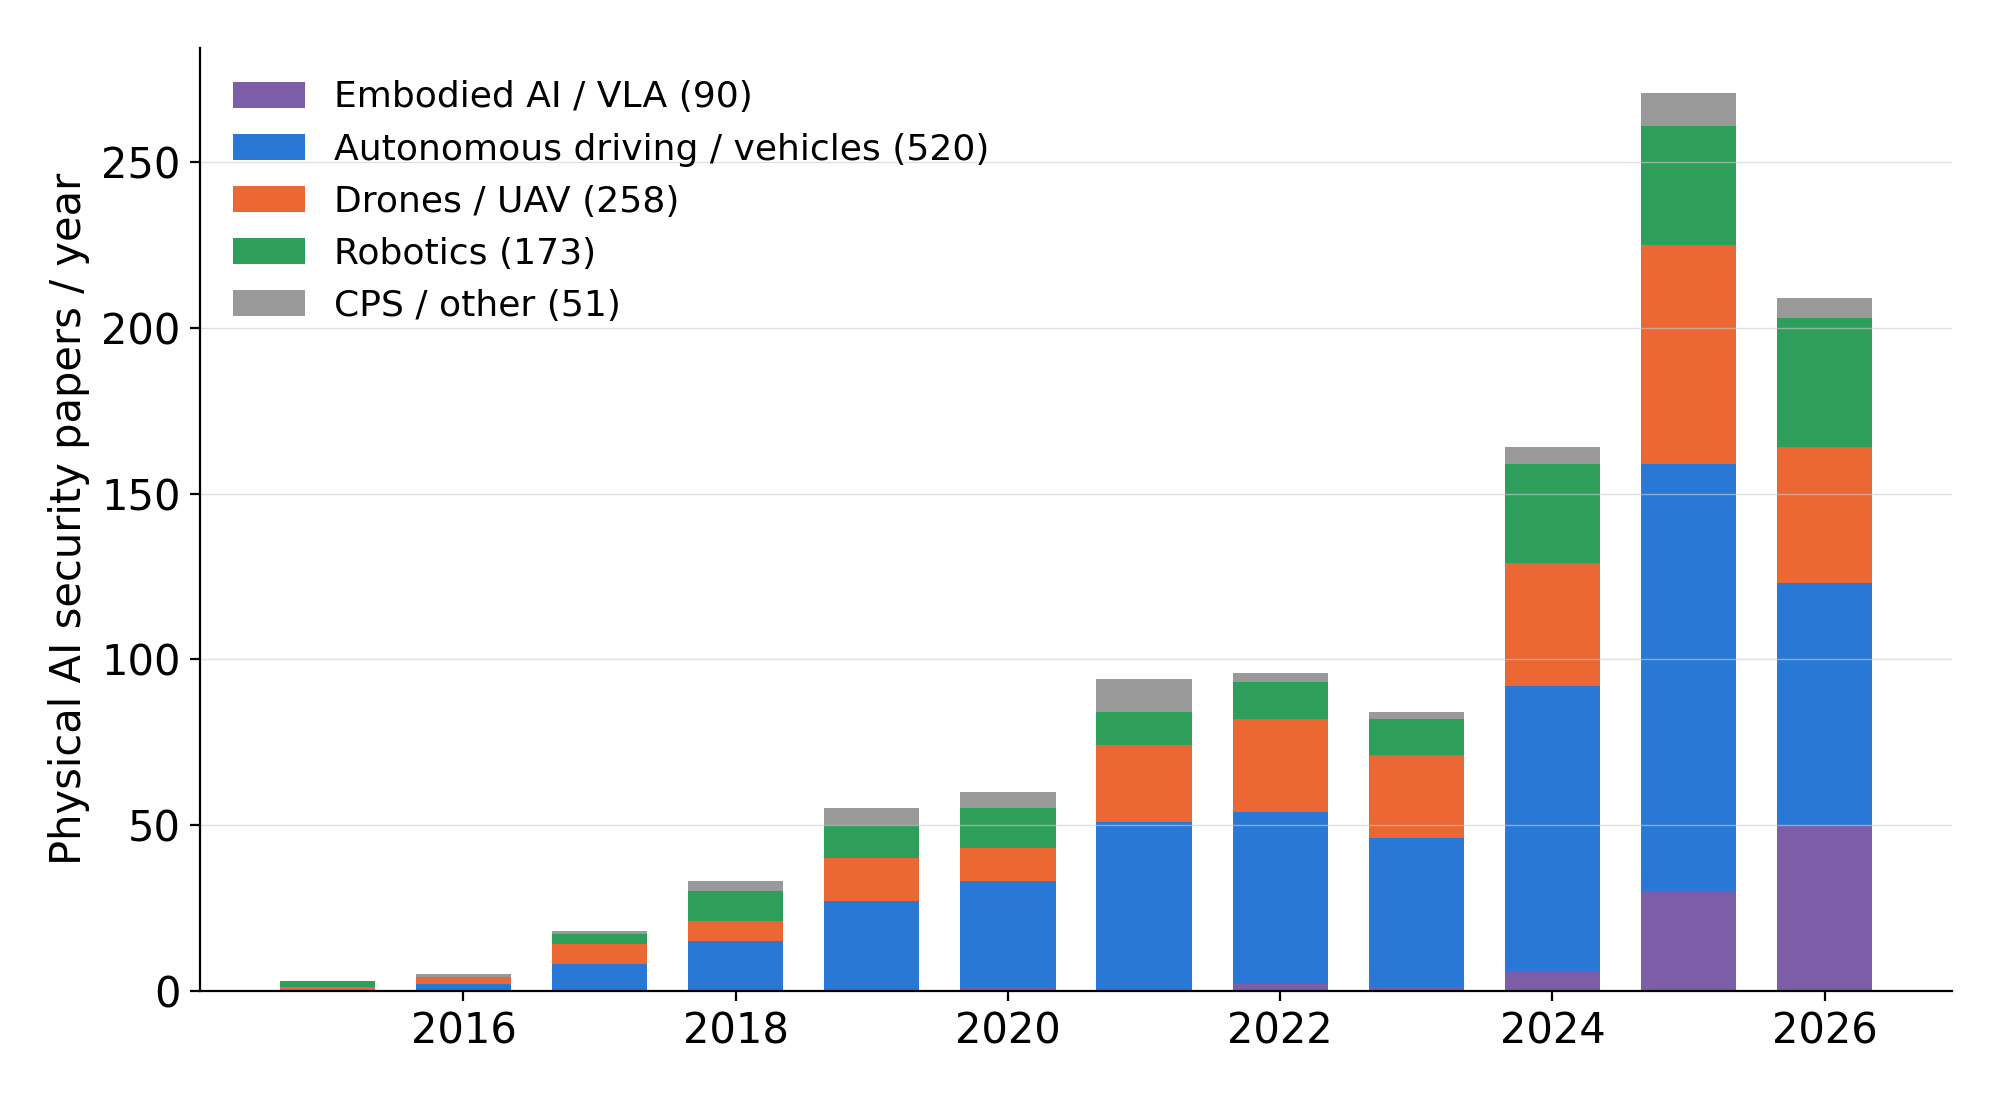
Physical AI Security Papers: a curated list of arXiv papers on the security (attacks and defenses) of AI-driven cyber-physical systems: autonomous driving, drones/UAV, robotics, and embodied AI. The list goes back to 2013 and is categorized by target platform.

Physical AI security papers per year by target category

Both pages are linked from the Projects menu. Comments and pointers to papers we may have missed are welcome.

A paper got accepted!

We are thrilled to announce that our conference paper entitled “Artistic Adversarial Examples: Graffiti-Based Adversarial Attacks on Traffic Sign Recognition” has been accepted for publication in The 28th International Conference on Information and Communications Security (ICICS 2026). This work is a fruit of our international collaboration with Politecnico di Milano. Congratulations to Zhuge-kun and kudos to the entire team!

In this work, we propose artistic adversarial examples — adversarial patches crafted to look like ordinary street graffiti so that they blend naturally into urban scenes. Combining a graffiti-trained generative model with a two-stage optimization that couples white-box latent optimization and black-box placement refinement, our attack degrades traffic sign detection while keeping the perturbations visually plausible. Extensive experiments across digital, simulated, and physical settings show that the generated graffiti substantially disrupts traffic sign recognition, achieving up to a 72.8% attack success rate with an average confidence drop of 65.8%.

Zhenghao Michele Zhuge, Go Tsuruoka, Zhihe Zhang, Stefano Longari, Lachlan Moore, Stefano Zanero, and Tatsuya Mori, "Artistic Adversarial Examples: Graffiti-Based Adversarial Attacks on Traffic Sign Recognition." In Proc. of The 28th International Conference on Information and Communications Security (ICICS 2026), Fukui, Japan, Oct 2026.