A paper got accepted!

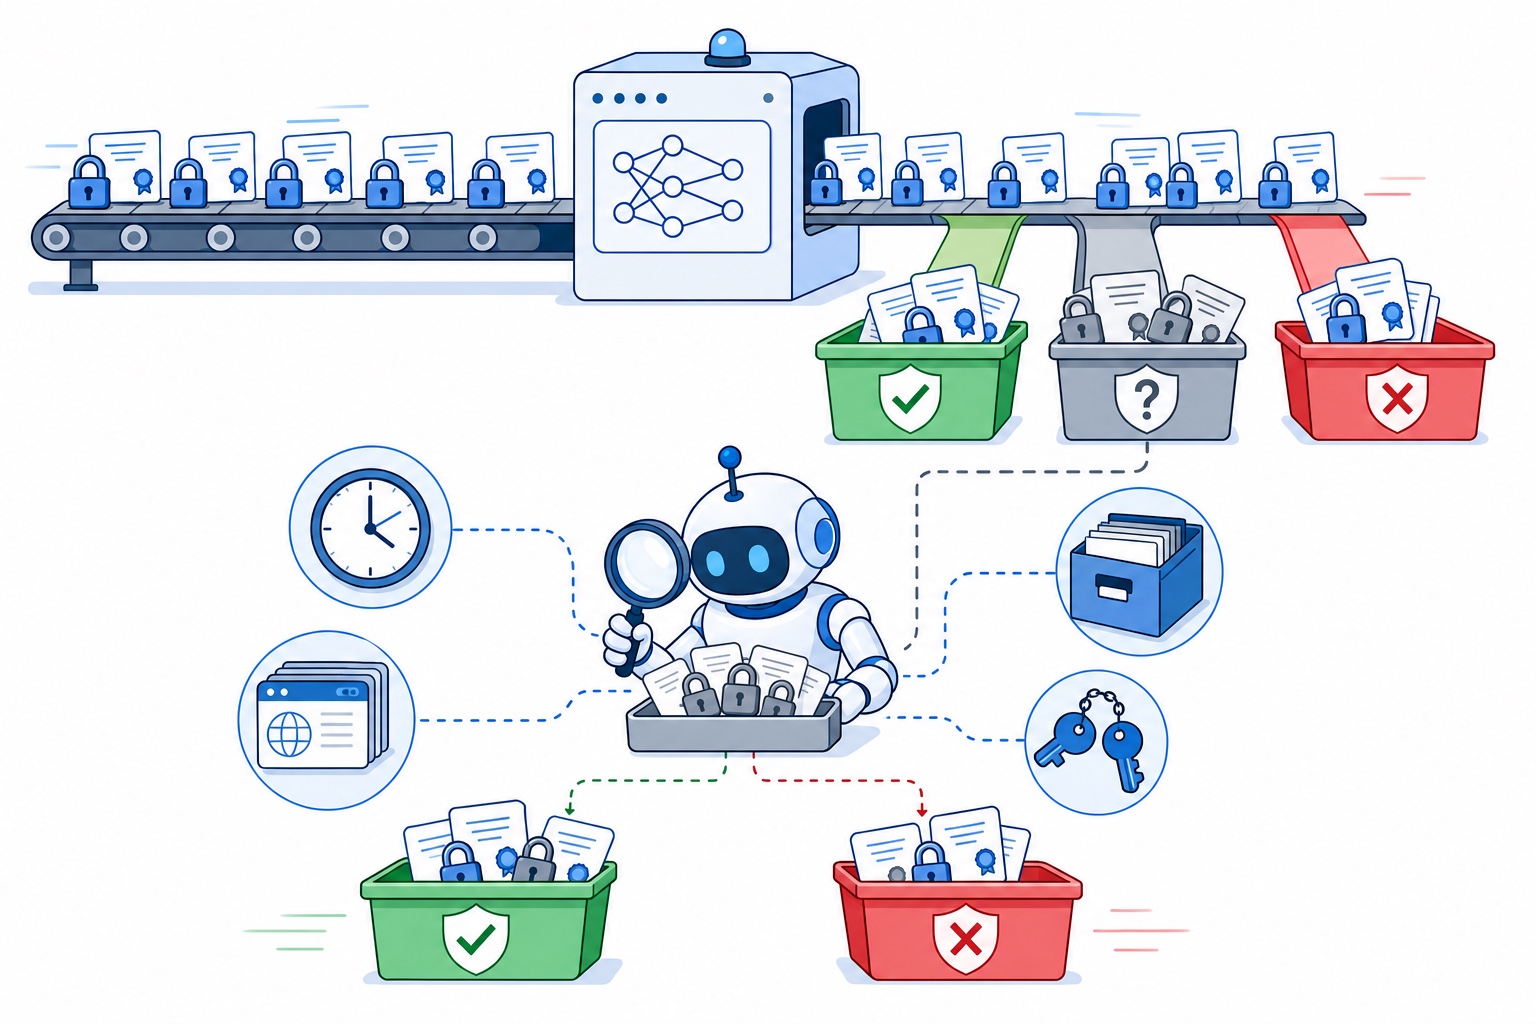
We are thrilled to announce that our journal paper entitled “Resolving the Classifier’s Gray Zone: A Tool-Augmented LLM Agent for Phishing Detection at Certificate-Issuance Time” has been accepted for publication in IEICE Transactions on Information and Systems, Special Section on Information and Communication System Security. Congratulations Asomura-san, and kudos to Iijima-san!

In this work, we tackle the gray zone of phishing detection: the domains that even a state-of-the-art supervised classifier cannot confidently assign to either class, where misses and false alarms concentrate. We propose a two-layer system in which high-confidence domains are decided automatically by machine learning and only the gray zone is handed to GrayLens, a tool-augmented LLM agent that reproduces an analyst’s investigation by combining Certificate Transparency issuance history, Wayback Machine archives, SubjectPublicKeyInfo (SPKI) sharing analysis, and brand impersonation detection, without fetching the target’s live page. On a gray-zone evaluation set of 24,633 domains, where XGBoost drops to F1 = 0.7334, the agent raises F1 to 0.9675 and cuts the miss rate from 36.4% to 2.5%. We also find that phishing domains share an SPKI hash with other domains 65.6% of the time, about 15 times the 4.4% rate of legitimate domains.

Ichiro Asomura, Ryo Iijima, and Tatsuya Mori. "Resolving the Classifier’s Gray Zone: A Tool-Augmented LLM Agent for Phishing Detection at Certificate-Issuance Time." IEICE Transactions on Information and Systems, Special Section on Information and Communication System Security, to appear (Jun 2027).
A paper got accepted!

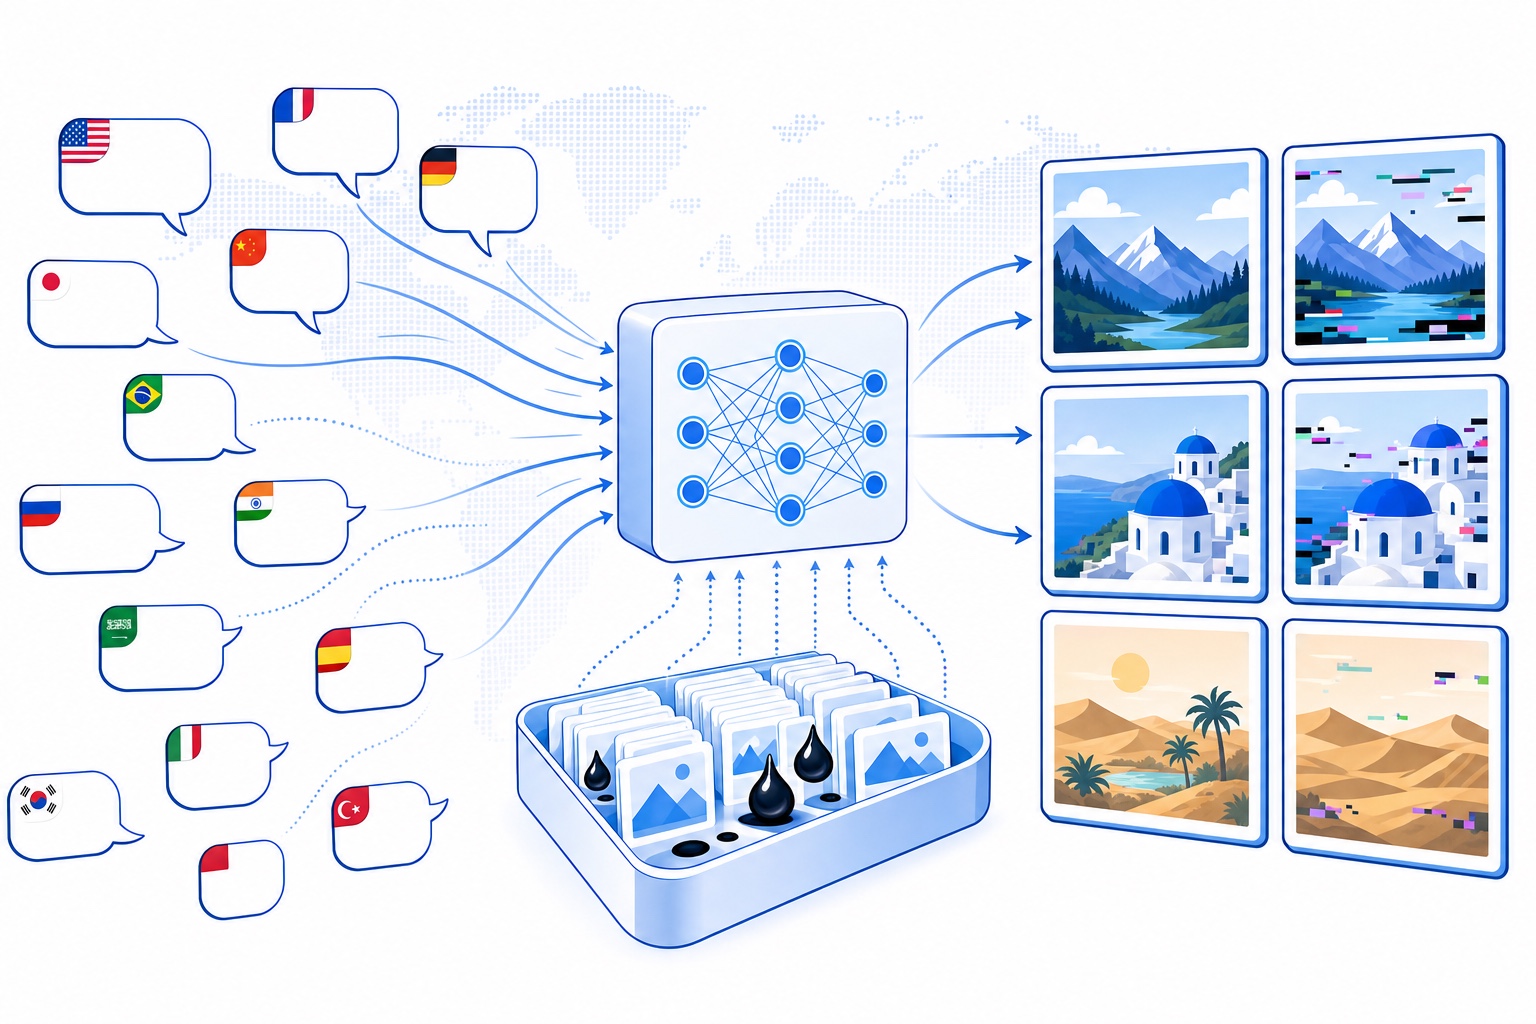
We are thrilled to announce that our journal paper entitled “Not All Languages Are Equally Safe: Evaluating Cross-Lingual Data Poisoning Attacks Against Text-to-Image Models” has been accepted for publication in IEICE Transactions on Information and Systems, Special Section on Information and Communication System Security. This paper is an extended version of our ICPR 2026 paper. Congratulations Kakebayashi-kun!

In this work, we systematically evaluate the vulnerability of text-to-image (T2I) models to data poisoning attacks across 10 languages. We show that poisoned data constructed in English transfers to non-English prompts, and that several languages, such as Indonesian, Japanese, and Turkish, are notably more vulnerable than English, on both Stable Diffusion v2 and SDXL. Our analysis indicates that syntactic and genetic distance from English, as well as weaker cross-lingual alignment of the text encoder, are associated with higher attack success rates. Finally, we show that fine-tuning the text encoder with non-English data to improve cross-lingual alignment can reduce attack success rates.

Ryohei Kakebayashi and Tatsuya Mori. "Not All Languages Are Equally Safe: Evaluating Cross-Lingual Data Poisoning Attacks Against Text-to-Image Models." IEICE Transactions on Information and Systems, Special Section on Information and Communication System Security, to appear (Jun 2027).
A paper got accepted!

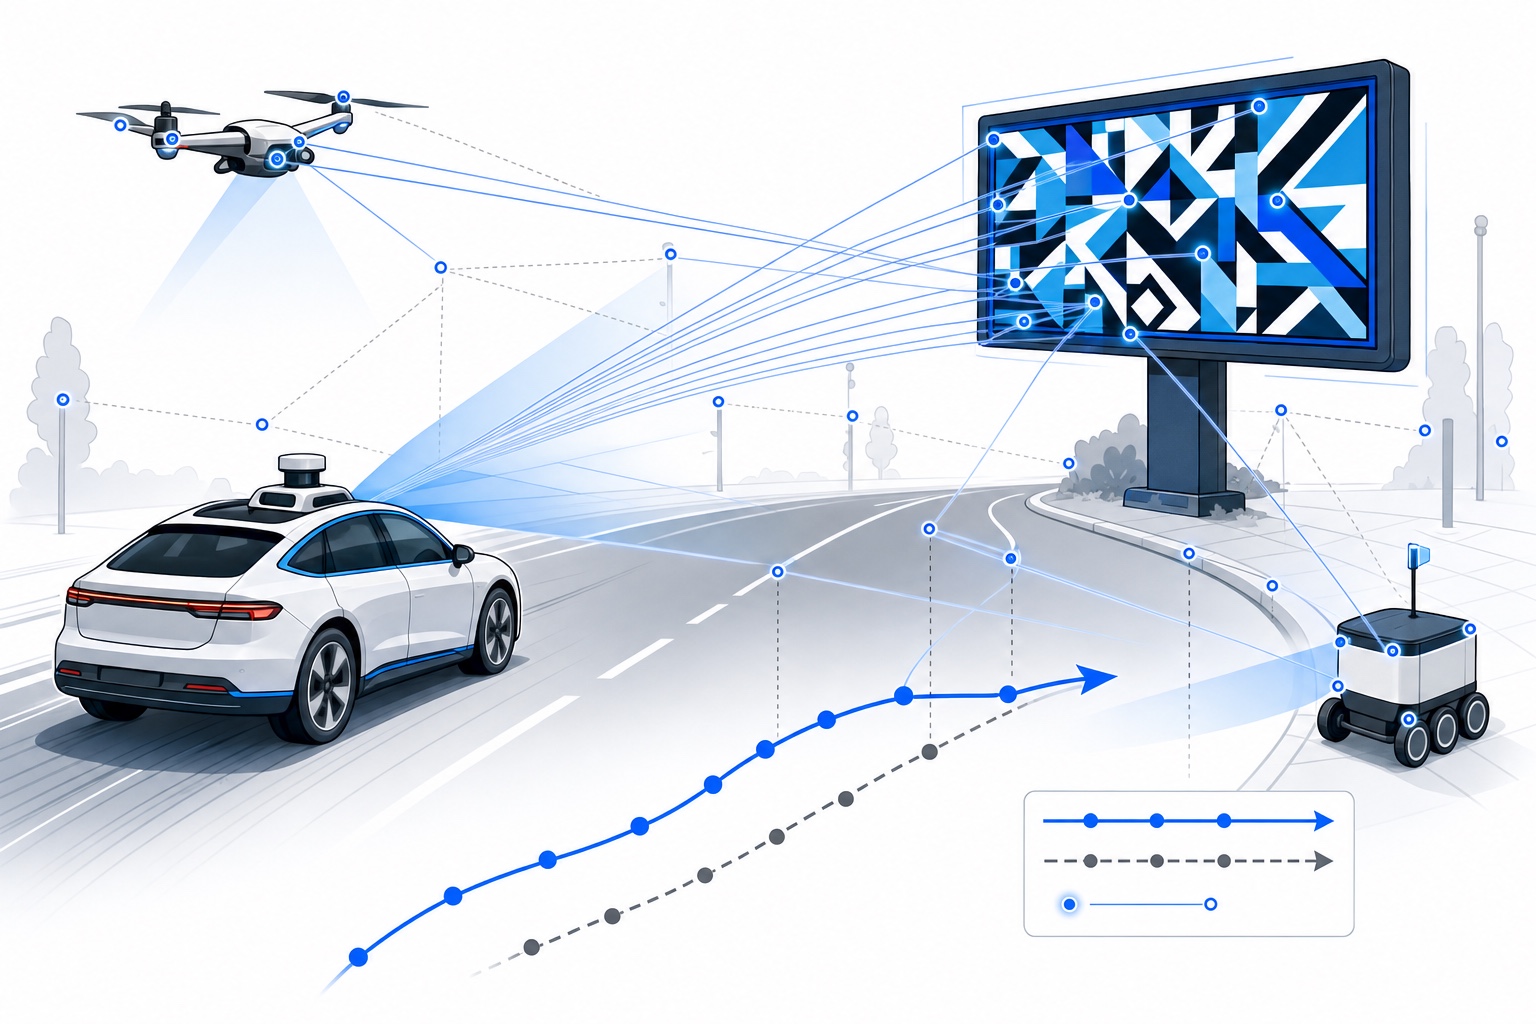
We are thrilled to announce that our journal paper entitled “DAP: Physically Realizable and Controllable Dynamic Adversarial Patch Attack Against Feature-based Visual Localization” has been accepted for publication in IEICE Transactions on Information and Systems, Special Section on Information and Communication System Security. Congratulations Zhang-kun and Peng-kun!

In this work, we present DAP (Dynamic Adversarial Patch), a physically realizable attack against feature-based visual localization, which underpins navigation in autonomous vehicles, mobile robots, and drones. By displaying dynamically changing content, DAP creates coherent, trackable feature correspondences that steer pose estimation in an attacker-chosen direction, while the feature-inducing structure is hidden inside ordinary advertisement content by an environment-adaptive generation pipeline. Evaluations in the CARLA simulator and in the real world across representative feature-based pipelines show that DAP induces systematic, directional drift with a stable inverse relationship between patch motion and trajectory deviation, and we examine lightweight pipeline-level mitigations that substantially reduce the effect.

Zhihe Zhang, Shuo Peng, and Tatsuya Mori. "DAP: Physically Realizable and Controllable Dynamic Adversarial Patch Attack Against Feature-based Visual Localization." IEICE Transactions on Information and Systems, Special Section on Information and Communication System Security, to appear (Jun 2027).
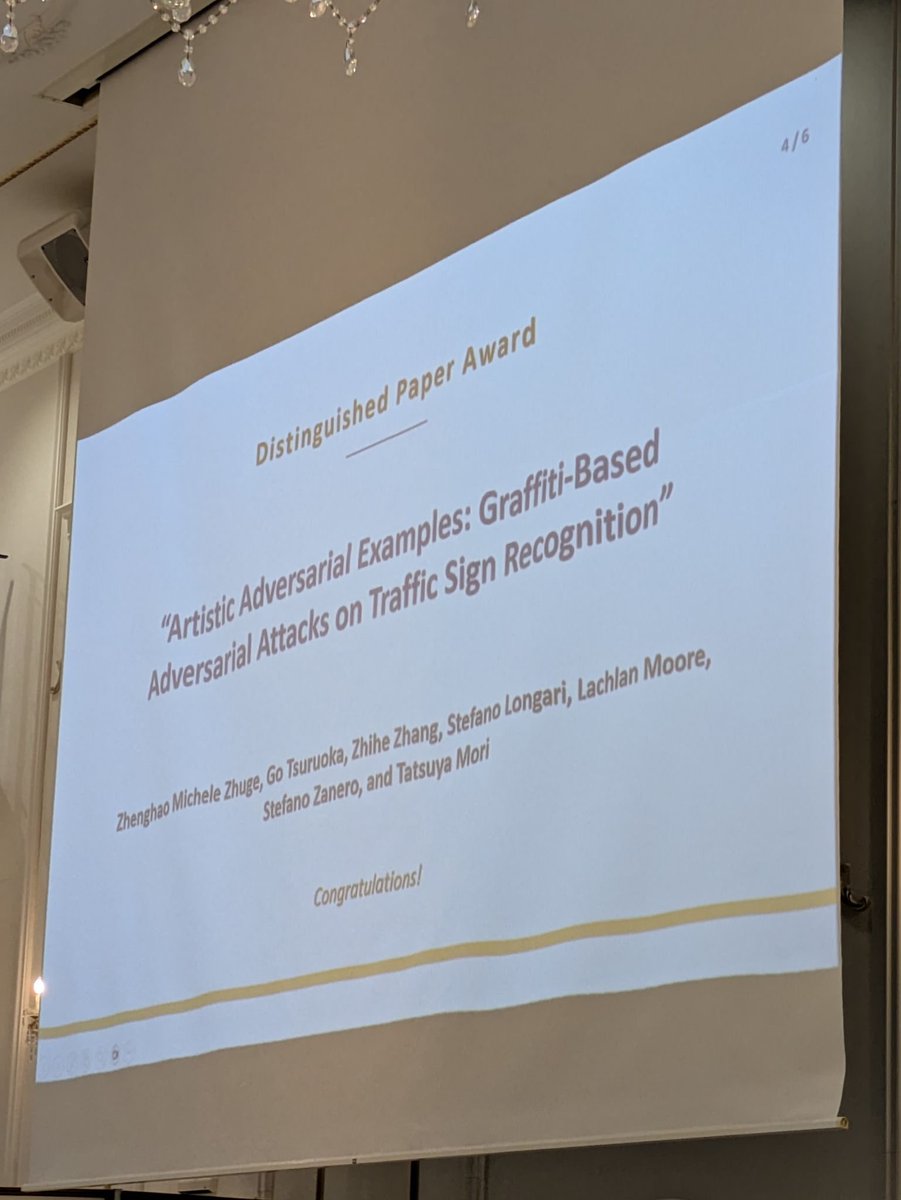
Distinguished Paper Award (ICICS 2026)

Distinguished Paper Award announcement slide at the ICICS 2026 closing ceremony
Award announcement at the ICICS 2026 closing ceremony in Fukui

We are delighted to announce that our paper “Artistic Adversarial Examples: Graffiti-Based Adversarial Attacks on Traffic Sign Recognition” received the Distinguished Paper Award at the 28th International Conference on Information and Communications Security (ICICS 2026), held in Fukui, Japan, on October 27–30, 2026. This work is a fruit of our international collaboration with Politecnico di Milano. Congratulations to Zhuge-kun, who led the work and presented it in Fukui, and kudos to the entire team!

In this work, we propose artistic adversarial examples — adversarial patches crafted to look like ordinary street graffiti so that they blend naturally into urban scenes. Combining a graffiti-trained generative model with a two-stage optimization that couples white-box latent optimization and black-box placement refinement, our attack degrades traffic sign detection while keeping the perturbations visually plausible. Extensive experiments across digital, simulated, and physical settings show that the generated graffiti substantially disrupts traffic sign recognition, achieving up to a 72.8% attack success rate with an average confidence drop of 65.8%.

Zhenghao Michele Zhuge, Go Tsuruoka, Zhihe Zhang, Stefano Longari, Lachlan Moore, Stefano Zanero, and Tatsuya Mori, "Artistic Adversarial Examples: Graffiti-Based Adversarial Attacks on Traffic Sign Recognition." In Proc. of the 28th International Conference on Information and Communications Security (ICICS 2026), Fukui, Japan, Oct 2026, pp. 198–219. Distinguished Paper Award [DOI][Springer]

コンピュータセキュリティシンポジウム(CSS 2026)で13件の研究発表と6件の受賞

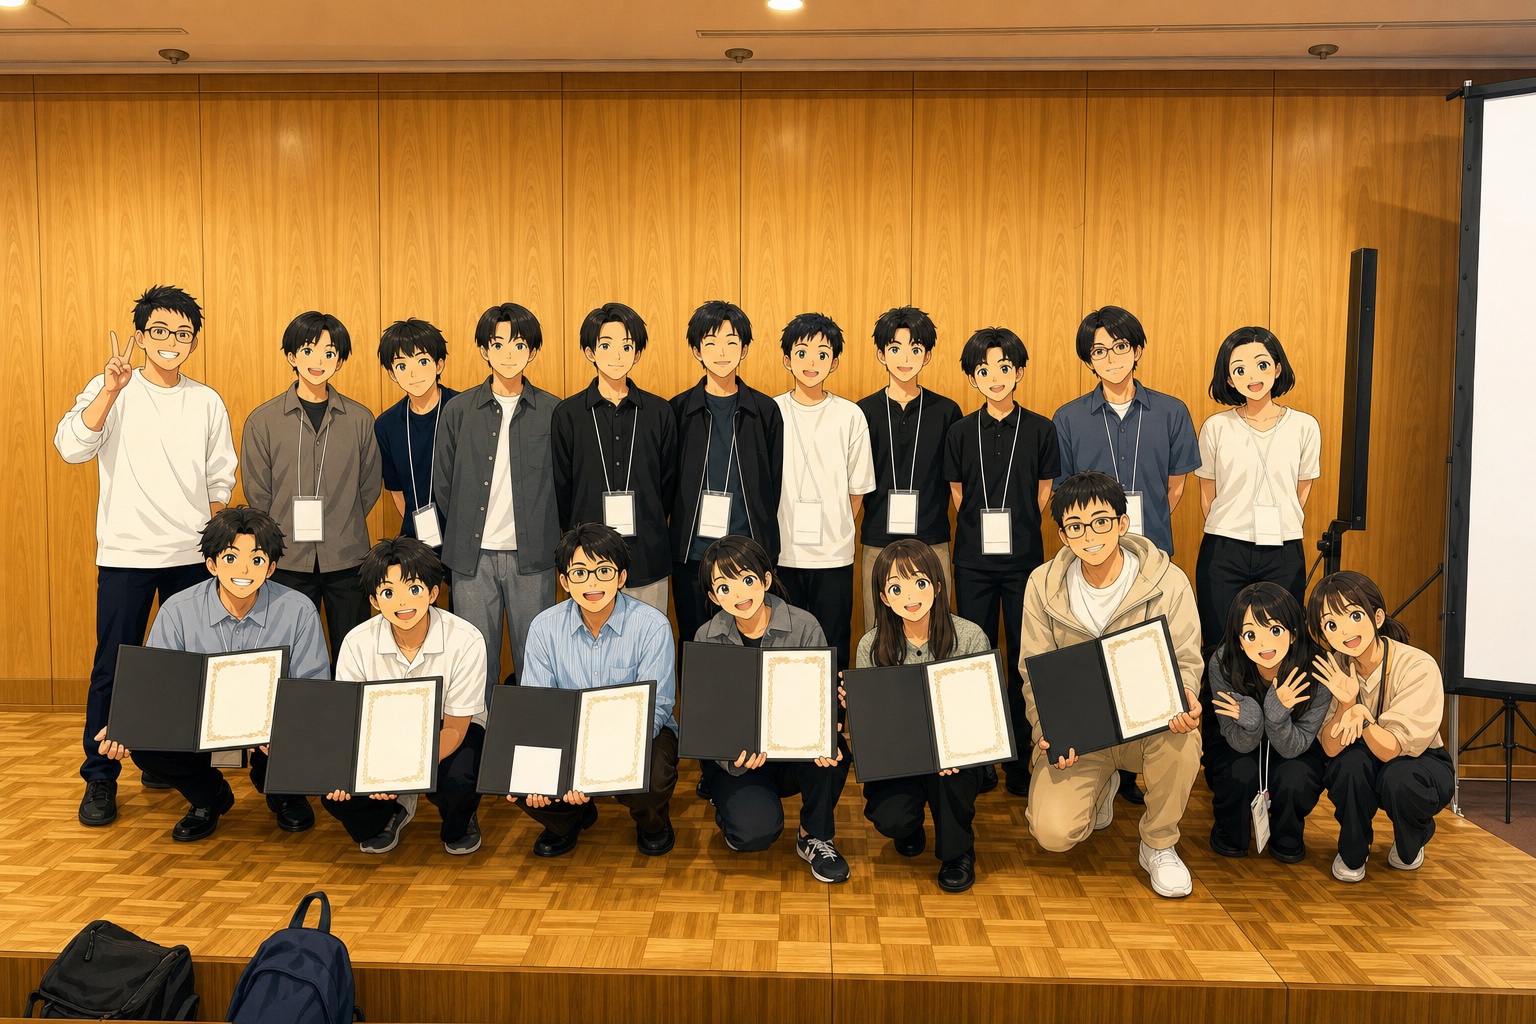
CSS 2026 表彰式後の集合写真(アニメ風に加工)

10月19日から23日まで浜松(アクトシティ浜松)で開催されたコンピュータセキュリティシンポジウム (CSS 2026) にて、当研究室から13件の研究を発表しました。この内、6件の発表に対して表彰を頂きました(優秀論文賞3件、学生論文賞2件、奨励賞1件)。受賞された皆さん、おめでとうございます!当日発表でのフィードバック、ならびに表彰等で奨励頂きましたことを糧に、次の研究につなげたいと思います。

  • Lachlan Moore, Yinan Zhao, Go Tsuruoka, Allan Wirth and Tatsuya Mori. “Investigating Privacy Transparency Gaps in Connected Vehicle Interfaces: A Think-Aloud Study Design.” コンピュータセキュリティシンポジウム 2026 論文集 (CSS 2026),2026年
  • Zhihe Zhang, Shuo Peng and Tatsuya Mori. “SoK: The Widening Gap Between Adversarial Patch Attacks and Modern Object Detectors.” コンピュータセキュリティシンポジウム 2026 論文集 (CSS 2026),2026年 (学生論文賞)
  • 海老根 佑雅, 野本 一輝, 鶴岡 豪, 田中 優奈, 森 達哉. “特徴点ベースvSLAMに共通する脆弱性を突く敵対的映像攻撃と防御手法の評価.” コンピュータセキュリティシンポジウム 2026 論文集 (CSS 2026),2026年 (優秀論文賞)
  • 小林 航太朗, 渡邉 卓弥, 高田 雄太, 熊谷 裕志, 神薗 雅紀, 森 達哉. “ブロックチェーンアドレスポイズニングにおけるクロスチェーン先回り攻撃と攻撃者戦略の分析.” コンピュータセキュリティシンポジウム 2026 論文集 (CSS 2026),2026年
  • 迫本 澪, 渡邉 龍星, 古橋 俊輝, 森 達哉. “悪性SIMアプレットによる通信チャネル占有攻撃の脅威評価.” コンピュータセキュリティシンポジウム 2026 論文集 (CSS 2026),2026年 (優秀論文賞)
  • 佐藤 光優, 鶴岡 豪, 野本 一輝, 田中 優奈, 森 達哉. “自動運転における HD マップ改ざん攻撃の体系化と End-to-End 評価.” コンピュータセキュリティシンポジウム 2026 論文集 (CSS 2026),2026年 (学生論文賞)
  • Shuo Peng, Zhihe Zhang, Go Tsuruoka and Tatsuya Mori. “Vehicle-Agnostic Multi-Class Attack Attribution on the CAN Bus.” コンピュータセキュリティシンポジウム 2026 論文集 (CSS 2026),2026年 (優秀論文賞)
  • 平井 航大, 田中 優奈, 野本 一輝, 鶴岡 豪, 森 達哉. “V2X に対する攻撃の体系的評価によるコンポーネントレベルとシステムレベルの乖離の検証.” コンピュータセキュリティシンポジウム 2026 論文集 (CSS 2026),2026年
  • 鶴岡 豪, 佐藤 貴海, 飯島 涼, 森 達哉. “ブラックホール攻撃: Occupancy Predictionを用いた自動運転に対するハイジャック攻撃の提案とその対策.” コンピュータセキュリティシンポジウム 2026 論文集 (CSS 2026),2026年 (奨励賞)
  • 斧田 洋人, 鶴岡 豪, 末次 響, 大西 健斗, 拓矢 東, 小関 義博, 中井 綱人, 森 達哉. “敵対的パッチによる偽障害物生成攻撃のシステムレベル評価.” コンピュータセキュリティシンポジウム 2026 論文集 (CSS 2026),2026年
  • Yinan Zhao, Lachlan Moore, Sara Rampazzi and Tatsuya Mori. “Detecting Sensor Attacks on Autonomous Vehicles through Latent Correlations.” コンピュータセキュリティシンポジウム 2026 論文集 (CSS 2026),2026年
  • 末次 響, 鶴岡 豪, 斧田 洋人, 田中 優奈, 野本 一輝, 森 達哉. “近傍の物体に擬態した敵対的パッチによるターゲット物体検出の妨害攻撃.” コンピュータセキュリティシンポジウム 2026 論文集 (CSS 2026),2026年
  • Jiadong Liu and Tatsuya Mori. “An Empirical Study of the Robustness of World-Model-Based Planning.” コンピュータセキュリティシンポジウム 2026 論文集 (CSS 2026),2026年